Products
Infralib: an open-source distribution for Kubernetes platforms
Released under the AGPL
Trusted by
- Tested releases every weekday
- Tested on live AWS, Google Cloud, Azure and Oracle accounts
- In production since 2020.
Don't write or wire the infrastructure yourself.
Across the production projects we've migrated, the IaC codebase shrank by 88% and thousands of lines collapse to a few hundred.
Patching CVEs is constant work. We ship tested updates every weekday.
Apply them when you're ready, instead of developing, testing and rolling out each patch yourself.
New features land in the open-source release as Infralib evolves.
Adopt them on your schedule, without funding the development yourself.
Why Infralib
Infralib keeps your applications, infrastructure and operations in one versioned codebase — so your platform stays consistent, portable and secure as it grows.
One codebase, not one fork per team
Different teams want different clouds, different security policies, different in-house tools. For years the only answer was forking the platform template per team and paying to maintain every fork. Infralib gives you one codebase that adapts to each:
- Runs on AWS, Google Cloud, Azure and Oracle Cloud
- Use only the modules you need, or bring your own
- Serves regulated industries without abandoning the shared codebase
The cloud underneath can change. Your operating model doesn't
Cloud providers ship components, not platforms. Infralib wraps them in an opinionated open-source layer so your operations are not dependent on which cloud sits underneath. This is what we mean by movability: the freedom to choose a vendor service without losing the ability to leave it.
- Place workspaces in the clouds and regions your regulations require.
- Spread critical workloads across providers.
- Use vendor-specific services when they earn it: as a deliberate choice, not a default.
Security you inherit, not implement
Infralib ships with security controls that most teams spend months implementing manually.
- Pod Security Admission enforces secure deployment practices across all workloads.
- Infralib meets the Estonian Information Security Standard (E-ITS) requirements for Very High data protection classification
- The default configuration exceeds 70% of the CIS AWS Benchmark out of the box.
Treat infrastructure like a software project
Forking platform templates is fast on day one and unaffordable on day five hundred. Infralib brings the patterns software engineers use (libraries, interfaces, dependency injection) to platform engineering.
Agent: the package manager and compiler
Reads your configuration, resolves dependencies, and generates pipeline definitions for AWS CodePipeline, Google CloudDeploy, or another pipeline engine.
Modules: the libraries
Pre-tested, versioned, built around clean interfaces. Swap any module for a custom implementation when corporate policy or an in-house tool requires it — the rest of the platform doesn't change.
Platform APIs: the cloud-agnostic interfaces
One interface for managed open-source services like PostgreSQL and Valkey, regardless of which cloud runs them underneath. Change providers without rewriting your applications.
Dependency injection: the wiring
Modules connect to each other automatically. Turn on AWS KMS, and Kubernetes uses it for all Persistent Volumes. Provision a VPC, and its subnets flow into the EKS module. You describe intent, not glue code.
What’s in the box
Infralib is an open-source platform distribution. Think of it as a Linux distribution or Homebrew for cloud infrastructure. It installs, configures and updates the open-source applications and cloud services that make up your Kubernetes platform, and wires them together so they work as one system.
Kubernetes for container orchestration
ArgoCD for GitOps
OpenTelemetry for logs, metrics and tracing
Crossplane for cloud resource provisioning
Managed open-source services: PostgreSQL, MariaDB, Valkey, Kafka, RabbitMQ
DNS & TLS orchestration
Integrates with your cloud infrastructure
Infralib is opinionated by default and customizable when your needs evolve. Every integration point is built on a standard interface so you can adopt the defaults or plug in what your organization already uses.
Typed module contracts
Modules declare structured inputs and outputs through typed contracts. The Infralib agent validates compatibility and wires dependencies automatically. Replace any module with a custom implementation that satisfies the same contract. The rest of the platform continues to work without changes.
Cloud-agnostic service APIs
One interface for managed open-source services like PostgreSQL and Valkey, regardless of which cloud runs them underneath. Applications talk to the API, not the cloud. Change providers or move between clouds without rewriting application configuration.
OpenTelemetry-based observability
Metrics, logs and traces are collected through OpenTelemetry, the industry standard for observability instrumentation. Route telemetry to the backend your organization already operates, whether that is Datadog, Splunk, or your own Grafana stack. Infralib handles collection and instrumentation; you choose where the data goes.
Standard identity providers
OpenID Connect integration across the platform. Plug in your existing identity provider: Entra ID, Okta, Google Workspace, or any OIDC-compliant service for single sign-on without a proprietary auth layer.
How Infralib compares
| Infralib | DIY (Terraform + Helm + ArgoCD) | OpenShift | Rancher | |
|---|---|---|---|---|
| Day one | Pre-wired Kubernetes platform: observability, GitOps, DNS/TLS, SSO | Empty repo | Curated commercial K8s platform with Red Hat's stack | K8s management plane with a curated app catalog |
| Ongoing updates | Releases tested every weekday on live clouds; you adopt them when ready | You patch CVEs and upgrade components yourself | Red Hat-controlled release cadence and supported versions | SUSE-controlled releases; community channels available |
| Customization | Override or replace any module; rest of platform unchanged | Total control, total ownership | Operator framework, within the Red Hat ecosystem | Helm-based catalog; broader stack flexibility than OpenShift |
| License | AGPL-3.0 | Free (component licenses vary) | Commercial (open-source core) | Apache 2.0 core; commercial support tier |
| Best match | If you operate multi-tenant or multi-cloud platforms and want a working platform on day one without funding the plumbing yourself | If you have the headcount and strong opinions about every layer of your platform | If you want an opinionated commercial Kubernetes platform with enterprise support and a single vendor on the contract | If you want a multi-cloud Kubernetes management plane with a curated application catalog |
Frequently asked questions
What is Infralib?
Infralib is an open-source distribution for Kubernetes platforms. It's a library of production-tested Terraform/OpenTofu modules and Helm charts covering networking, Kubernetes clusters, autoscaling, ArgoCD, ingress, observability, DNS and TLS, secrets and more. You describe your platform in one YAML file, and the Infralib agent provisions it and keeps it up to date.
Is the Infralib agent an AI agent?
No. The agent is a command-line tool written in Go. It reads your config, resolves module versions and dependencies, creates the pipelines in your cloud account and runs them. It doesn't use an LLM.
Which clouds does Infralib support?
AWS, Google Cloud, Microsoft Azure and Oracle Cloud Infrastructure. Each has its own modules for networking, managed Kubernetes (EKS, GKE, AKS, OKE), DNS and key management. The Kubernetes-level modules (ArgoCD, observability, ingress, security) are shared across all of them.
Is Infralib really free?
Yes. Infralib and the agent are released under the AGPL-3.0 licence. Using them to run your own infrastructure carries no obligation to publish anything: the licence covers Infralib itself, not the infrastructure it creates or the applications you run on it. The obligations only apply if you modify Infralib and offer it to others as a network service, or redistribute a modified version. For commercial licensing, contact us.
What do I need to get started?
You need:
- An account with one of the supported clouds, and credentials with admin rights for the first run
- Docker, or Go to install the agent
- A YAML file describing your platform
The quickstart guide and full documentation are at docs.entigo.com.
How do updates work?
New releases are tested against live cloud accounts before they're published. When you run the agent's update command, it moves your modules to the latest tested release and shows you a plan first. By default, updates that would remove resources wait for manual approval, and you can make the approval rules stricter for each step. You can also run updates on a schedule, or pin specific versions.
Can we roll back an update?
Yes, if the change can be reversed. You can pin a module to an earlier version and the agent will apply it. Some changes can't be undone, such as a Kubernetes version upgrade, so always review the plan before approving.
Do we have to use every module, or the agent?
No. You can include or exclude modules in your config, or replace a module with your own implementation as long as it keeps the same inputs and outputs. You can also skip the agent and use released modules directly from Terraform/OpenTofu, or deploy the Helm charts from ArgoCD.
Can we move our existing infrastructure to Infralib?
Yes. The agent includes migration commands that map your existing OpenTofu/Terraform state onto Infralib modules and check the resulting plan, so you can adopt Infralib without rebuilding from scratch.
Does Entigo get access to our infrastructure?
No. The agent runs in your own cloud account and keeps its state in your own storage bucket. Your configuration, infrastructure and applications stay with you.
How is Infralib different from Entigo Platform?
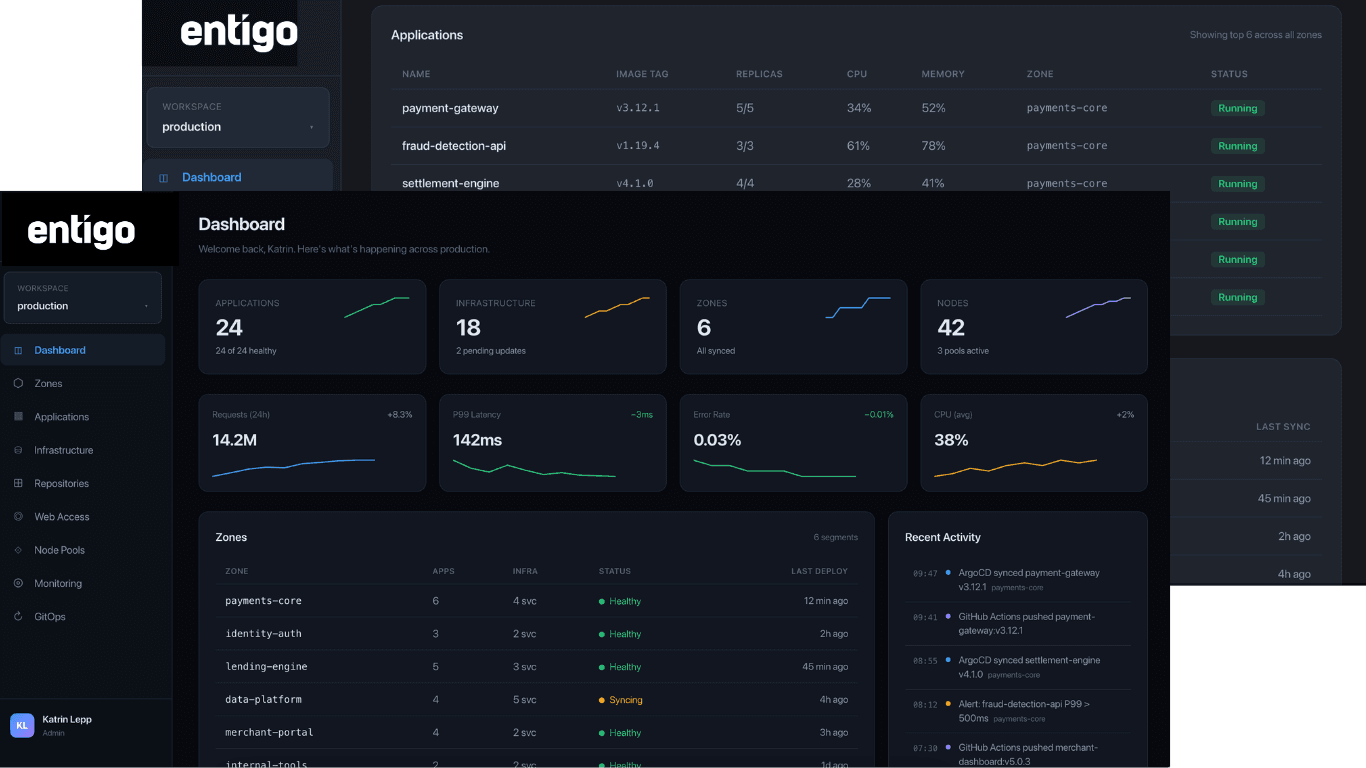
Infralib is the open-source foundation you install and run yourself. Entigo Platform is our commercial managed control plane built on Infralib. It adds a workspace overview, developer self-service, cost visibility and compliance features, and we can operate it for you. Infralib works fully on its own and doesn't depend on Entigo Platform.
Who maintains Infralib, and can we get support?
Infralib is developed and maintained by the Entigo team. It has been in production since 2020 and is used by Estonian public-sector organisations including the Information System Authority (RIA) and TEHIK. If you need help with setup, migration or day-to-day operations, we offer support and engineering services, as well as the managed Entigo Platform.
Infralib is free to use under the AGPL
Start with the modules, run the agent, and have a working platform in under a day.
Entigo Platform
Operating Infralib at scale?
Entigo Platform is the managed control plane that builds on Infralib.